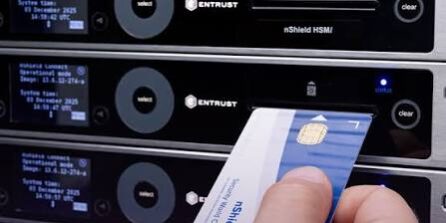
A hardware security module (HSM) is a hardware unit that stores cryptographic keys to keep them private while ensuring they are available to those authorized to use them. The primary objective of HSM security is to control which individuals have access to an organization’s digital security keys.
With HSM encryption, you enable your employees to use your private keys without granting them direct access. Used this way, HSMs help reduce your attack surface.
How do hardware security modules (HSMs) work?
Hardware security modules prevent an application from loading a copy of a private key into the memory of a web server. This is useful because while on a web server, your security keys are vulnerable to hackers. If an attacker gains access to the web server, they can locate your key and then use it to access sensitive data.
But by deploying either your own HSM system or an HSM-as-a-Service model, you close the door on hackers attempting to get their hands on your organization’s data.
The cryptographic functions involved in securing data during transmission all occur within the HSM environment, where data is shielded from attackers. The way an HSM is designed makes it impossible for an attacker to impact the processes happening inside the hardware unit. In other words, although an HSM is able to accept inputs from users, users have no access to its inner workings. This makes HSMs a secure solution for both storing your cryptographic keys and performing encryption/decryption procedures.
Types & Deployment Models of Hardware Security Modules
There are two primary types of HSMs: general purpose and payment hardware security modules.
Types of HSM based on purpose
1. General purpose hardware security modules
General purpose hardware security modules use common encryption algorithms and are mainly used with crypto wallets, public key infrastructure (PKI), and in the security of basic sensitive data. Some of the common algorithms general purpose HSMs use include CAPI, PKCS#11, CNG, and others.
2. Payment hardware security modules
Payment—or payment and transaction—HSMs are designed to protect credit and payment card information, as well as other sensitive information involved in financial transactions. These types of HSM play a significant role in the protection of payment information, helping organizations comply with Payment Card Industry Data Security Standards (PCI DSS).
2 types of HSM deployment models
You have two basic options with HSM: physical devices and cloud-based HSMs.
1. Physical devices
While all HSMs are physical devices, the term “physical HSM” refers to a unit you purchase and keep somewhere you choose, such as in an on-premises data center. In this case, you purchase the HSM outright and handle its deployment and management throughout its life cycle.
2. Cloud-based HSMs
A cloud-based HSM is still a physical device but is kept in a cloud data center, which houses the components that make up a cloud environment. With a cloud-based HSM, you either rent an HSM from the cloud provider or you pay to access its functionalities as needed.
6 Benefits of HSMs for Enterprise IT & Data Security
HSMs enhance enterprise and data security by safeguarding cryptographic keys and ensuring that sensitive information is encrypted, managed, and accessed only by authorized users. They reduce the risk of key compromise and strengthen overall IT infrastructure protection.
Here are the key benefits HSMs offer:
- Strong encryption keys: HSMs create random, high-strength keys and automatically rotate them. This makes it challenging for attackers to compromise encrypted data.
- Tamper detection: HSMs are tamper-resistant and detect unauthorized attempts. They automatically trigger alarms or lock down, thereby preventing key theft or misuse.
- Regulatory compliance and policy enforcement: HSMs help organizations maintain compliance while enforcing internal security policies by adhering to standards like FIPS 140-2 (Federal information processing standard).
- Secure hardware: All encryption, decryption, and key management operations occur inside the HSM. This ensures that private keys never leave the secure environment.
- Audit-ready logs: HSMs record every key usage and operation, providing detailed, audit-ready logs for accountability, regulatory reporting, and forensic investigations.
- Zero-trust environments: HSMs enable secure authentication, encryption, and key validation within zero-trust architectures.
Use Cases of HSMs
There are many different use cases for HSMs, all of which involve encrypting and decrypting sensitive or private information. Some of the more popular examples include:
- Protection of privileged access and company secrets: You can limit the effectiveness of insider threats with an HSM. That is because no one can tangle with what is happening inside an HSM—not even a capable internal hacker. Also, if your DevOps team needs to access private information, you can manage that access using an HSM to prevent exfiltration.
- Keys management: HSMs are very effective at managing cryptography keys. Whether deployed on-premises or in a cloud environment, HSMs give you the ability to manage multiple keys.
- Authentication and identity management: An HSM authenticates each user against required credentials and facilitates the creation of trustworthy identity credentials for securing your organization’s infrastructure.
- Public key infrastructure (PKI) and certificate authority (CA): HSMs secure CA keys and ensure the integrity of digital certificates and electronic signatures. This protects the trustworthiness of the entire PKI ecosystem from unauthorized access or compromise.
- Code signing: HSMs safeguard cryptographic keys used for digitally signing software code, thus verifying its authenticity and preventing tampering. Besides, they enforce strict access controls to prevent unauthorized code signing activity.
- Blockchain applications: HSMs protect cryptographic keys for signing blockchain transactions, ensuring integrity and non-repudiation. Moreover, they secure consensus mechanisms in permissioned blockchains, restricting validation to authorized participants only.
HSM vs TPM Modules for Encryption
HSMs are different from trusted platform modules (TPMs) even though both are physical devices and involve data encryption. An HSM is a removable unit that runs on its own, while a TPM is a chip on your motherboard that can encrypt an entire laptop or desktop disk.
Both TPMs and HSMs provide hardware-based protection for cryptographic operations. However, they differ in scope and capabilities.
For instance, TPM ensures system integrity by supporting secure boot, device authentication, and local key storage. It works at the device level to protect sensitive information used by operating systems and applications. On the other hand, HSM provides enterprise-grade security by storing and managing large volumes of cryptographic keys in a tamper-resistant environment. It is optimized for high-speed encryption, decryption, and digital signing.
Moreover, TPMs are lightweight, embedded chips, whereas HSMs are standalone devices (or cloud services) designed for scalability, compliance, and integration with multiple applications.
Here’s a quick comparison table differentiating between HSM and TPM.
| Factor | TPM | HSM |
| Purpose | Device security, boot trust, local key storage | Enterprise security, large-scale crypto operations |
| Deployment Scope | Embedded in PCs, laptops, and servers | Standalone appliances, PCI cards, or cloud |
| Performance | Limited crypto power, basic system functions | High-speed encryption, decryption, and signing |
| Key Management | Local key storage with limited capacity | Advanced lifecycle management in secure hardware |
| Integration & Flexibility | Works with OS and firmware | Integrates with apps, APIs, PKI systems |
Best Practices to Maximize HSM Security and Compliance
- Secure the physical environment: HSMs should be placed in a controlled location with restricted access and environmental monitoring. This helps avoid hardware failure. Besides, organizations should prioritize devices with tamper detection since they trigger key erasure in case of tampering. Moreover, teams should conduct regular physical inspections to identify signs of compromise that automated alerts may miss.
- Enforce strong key management policies: The efficacy of HSM depends on robust key management processes, starting with the use of true random number generators for high-entropy keys. Strong access controls, audit logging, and multi-factor authentication ensure that only authorized users can access or manage keys.
- Maintain operational security standards: Organizations should keep HSMs updated with patches and firmware updates. This approach helps address vulnerabilities promptly. Besides, staff managing HSMs need consistent security awareness training to follow secure key-handling workflows. Moreover, comprehensive logging and monitoring of all activity can enable faster detection of suspicious behavior and reduce risks of unnoticed cyberattacks.
- Align with compliance requirements: HSM deployments should align with recognized standards like FIPS 140-2 or common criteria to demonstrate validated security controls. Regulated industries, such as finance or healthcare, should comply with frameworks like PCI DSS (payment card industry data security standard) or HIPAA (health insurance portability and accountability act).
- Strengthen network security controls: Teams should protect communication between HSMs and other systems via firewalls, encryption, and network segmentation. Strong network controls reduce the risk of interception or manipulation during data exchange.
- Implement disaster recovery and audit plans: A disaster recovery plan is crucial for restoring HSM functionality and keys after an outage or incident. Secure and encrypted backups should be kept off-site but never stored on the same network. Besides, periodic audits by qualified professionals verify that all best practices remain intact.
Protect Encryption Keys and Simplify Compliance With HSMs
A hardware security module (HSM) safeguards an enterprise’s most critical cryptographic operations. It isolates and protects encryption keys, thereby reducing the risk of insider threats and external cyberattacks. Moreover, HSMs ensure compliance with strict data security standards, making them vital for regulated sectors, such as finance, government, and healthcare. Furthermore, HSMs strengthen enterprise resilience by enabling secure authentication, digital signing, and transaction protection at scale.
However, HSMs alone are not enough to defend against increasingly complex cyberattacks. That’s when organizations need solutions like Fortinet’s next-generation firewall (NGFW). It can help build complete protection across networks and applications and provide complementary security controls with advanced threat detection, inspection, and enforcement.
SSL inspection without an HSM can expose private keys and weaken encrypted traffic security. Strengthen security with FortiGate Firewall.